Security & Trust · Last reviewed October 5, 2026
SOC 2 Readiness Checklist for SaaS Startups
A SaaS startup is ready for SOC 2 when it can freeze a system boundary, put the Security criteria in scope, name one owner for every control area, and show evidence that real controls (MFA, access reviews, code review, logging, vendor reviews, incident response) already run day to day. Once that is true, choose a Type 1 or Type 2 report based on what your buyers ask for, and engage a licensed, peer-reviewed CPA firm. The checklist below walks through each step, maps evidence to the CC1–CC9 common criteria, and adds the auditor checks that matter after the AICPA’s 2026 warnings about “fast and easy” SOC reports.
What SOC 2 is (and is not)
Takeaway: SOC 2 is a CPA firm’s examination report on your controls, not a certificate you pass once.
According to the AICPA & CIMA SOC 2 resource page, a SOC 2 examination reports on controls at a service organization relevant to security, availability, processing integrity, confidentiality, or privacy. The report goes to customers and prospects who need assurance about those controls, usually under NDA.
- No AICPA badge. You hire a CPA firm, it examines a defined system, and it issues a report for a point in time (Type 1) or a period (Type 2).
- The criteria are the Trust Services Criteria (TSC). As of October 5, 2026, the AICPA page still lists the 2017 Trust Services Criteria (With Revised Points of Focus – 2022). The AICPA states the 2022 revisions changed points of focus and did not alter the criteria themselves.
- The system description has its own criteria. The same AICPA page lists the 2018 SOC 2 Description Criteria (With Revised Implementation Guidance – 2022), which governs what your management description of the system must cover.
- Policies must match practice. Auditors test design, and for Type 2 they also test whether controls operated. A policy nobody follows becomes an exception in the report.
Is your startup ready? Signals for and against
Takeaway: Start when buyers are asking and your basic controls already exist; otherwise fix hygiene first.
| Start now if… | Wait if… |
|---|---|
| Security questionnaires or procurement reviews are stalling revenue | No buyer has asked and runway is thin |
| Enterprise prospects list SOC 2 (often Type 2) as a contract prerequisite | You are mid-rewrite or swapping cloud accounts, so there is no stable system boundary |
| MFA, least-privilege cloud access, code review, and logging already run | Policies would be fiction: no MFA enforcement, no PR review, no offboarding process |
| You can freeze products, infrastructure, data stores, and subprocessors for a quarter | You expect a report “in two weeks” with no existing controls |
If the real blocker is legal paperwork (DPA, privacy policy, terms), clear that first with the SaaS legal documents checklist. SOC 2 is also not ISO 27001, HIPAA, or “GDPR compliance”; the controls overlap, but buyers treat them as separate programs.
Trust Services Criteria scope for a first report
Takeaway: Put Security in scope and add other categories only when a contract or live RFP requires them.
| Category | What it covers | First-report default | Add it when |
|---|---|---|---|
| Security (common criteria CC1–CC9) | Protection against unauthorized access; control environment, risk, access, operations, change, vendors | Always in scope | Required in every SOC 2 report |
| Availability (A1) | System availability as committed: capacity, backup, recovery | Often later | You sign uptime SLAs or customers are downtime-sensitive |
| Confidentiality (C1) | Information designated confidential is protected and disposed of as committed | Case by case | You make confidentiality commitments beyond general security |
| Processing integrity (PI1) | Processing is complete, valid, accurate, timely, and authorized | Usually later | Processing accuracy is the product (billing, payments, data pipelines) |
| Privacy (P1–P8) | Personal information collected, used, retained, disclosed, and disposed of per commitments | Usually later | Buyers require privacy assurance; overlaps with a privacy program |
Every category you add expands policies, evidence, and testing. Adding Availability before you have monitoring and incident metrics creates audit work without helping the deal.
SOC 2 compliance checklist by common criteria (CC1–CC9)
Takeaway: If you can produce the evidence in this table today, you are close to ready for a Security-only report.
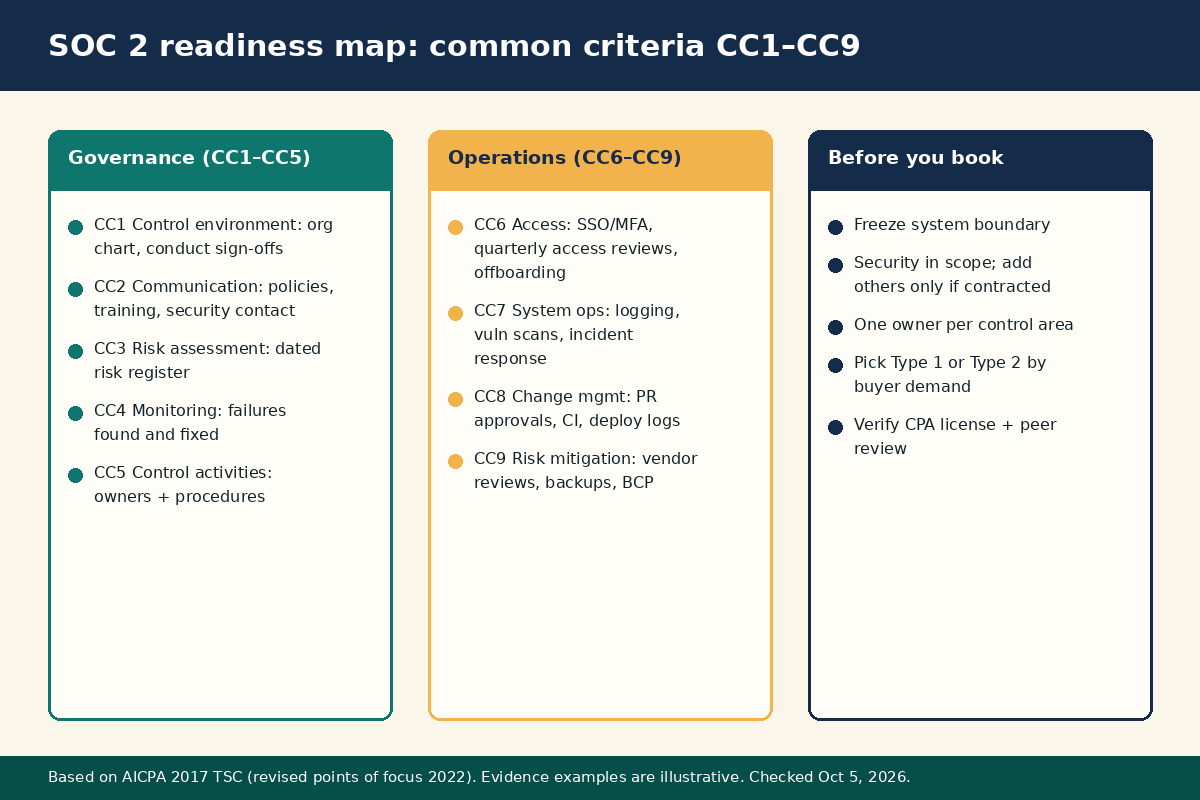
The Security category is built from nine common-criteria series in the 2017 TSC. The “what to have ready” column is our founder-level reading of typical evidence, not an official AICPA list; your auditor decides what is sufficient for your system.
| Series | Theme | What to have ready | Usual owner |
|---|---|---|---|
| CC1 | Control environment | Org chart, code of conduct acknowledgments, background-check process, security responsibilities in job descriptions | Founder / People |
| CC2 | Communication and information | Published security policies, internal security training records, customer-facing security contact and commitments | Founder / Security lead |
| CC3 | Risk assessment | Dated risk register, annual risk assessment notes, fraud risk considered | Founder / COO |
| CC4 | Monitoring activities | Evidence that control failures are detected and fixed (tickets, review sign-offs, internal checks) | Security lead |
| CC5 | Control activities | Policies that assign controls to people and technology; documented procedures | Security lead |
| CC6 | Logical and physical access | SSO/MFA enforcement, quarterly access reviews, joiner/mover/leaver tickets, encryption settings, device management | Eng / IT lead |
| CC7 | System operations | Logging and alerting, vulnerability scans with remediation records, incident response plan plus tabletop or real incident tickets | Eng on-call owner |
| CC8 | Change management | PR approvals, CI checks, deploy logs, emergency-change process | Eng lead |
| CC9 | Risk mitigation | Vendor and subprocessor inventory, vendor security reviews, business continuity and backup tests, insurance where relevant | Ops / Founder |
Evidence owners matrix (assign before tooling)
Takeaway: Every control area needs one accountable person, even when one person covers several rows.
| Control / evidence area | Accountable owner | Systems of record | Evidence examples |
|---|---|---|---|
| Access control and joiner/mover/leaver | Eng / IT lead | IdP (Okta, Google), GitHub, cloud IAM | Access reviews, MFA exports, offboarding tickets |
| Change management / SDLC | Eng lead | GitHub/GitLab, CI, ticketing | PR approvals, deploy logs, linked change tickets |
| Vulnerability and patch management | Eng / Security | Cloud provider, scanner, endpoint tool | Scan results, remediation timelines, patch records |
| Risk assessment and policies | Founder / COO | Policy hub, risk register | Signed policies, annual risk review |
| Vendors / subprocessors | Ops | Vendor list, contracts folder | Inventory, vendor SOC reports, DPAs |
| HR security | Ops / People | HRIS, training tool | Onboarding checklists, training completion |
| Incident response | Eng on-call owner | Paging, status page, runbook | IR plan, tabletop notes, incident tickets |
| Customer trust and questionnaires | Founder or sales engineer | Trust page, shared drive | Answer library, report-sharing process |
If nobody owns access reviews and change management, do not start a Type 2 period yet, whatever date sales has promised.
Should you start with SOC 2 Type 1?
Takeaway: Take a Type 1 when a deal cannot wait and buyers accept design-only assurance; go straight to Type 2 when they don’t.
| Report | What the CPA examines | Good fit |
|---|---|---|
| Type 1 | Description and suitability of control design as of a specific date | First enterprise deals that accept a design-only report while you build operating history |
| Type 2 | Design plus operating effectiveness over a defined period | Most enterprise security reviews and renewals once you can support a review period |
Many startups run readiness, take a Type 1 to unblock a deal, then start a Type 2 period. Others skip Type 1 when the first serious buyer already demands Type 2. We cover the trade-offs in detail in SOC 2 Type 1 vs Type 2.
How long does SOC 2 take?
Takeaway: Readiness can take weeks; a first Type 2 report usually takes months because the review period itself runs for months.
| Phase | What happens | Planning range |
|---|---|---|
| Readiness / gap closing | Scope memo, owners, policies, fix gaps (MFA, logging, offboarding) | A focused sprint of about 30 days if basics exist; longer if they don’t |
| Type 1 fieldwork and report | Auditor tests design as of a date, then drafts the report | Set with your CPA firm |
| Type 2 review period | Controls must operate consistently; evidence accumulates | The AICPA does not set one fixed length; practitioners commonly describe 3–12 months, and later reports usually cover 12 |
| Type 2 fieldwork and report | Sampling, testing, exceptions, management responses, final report | Set with your CPA firm after the period ends |
Treat any promise of a full SOC 2 report in a few days with suspicion; see the auditor checklist below.
30-day SOC 2 readiness checklist
Takeaway: Use the first month to make policy and practice match, not to collect screenshots.
- Days 1–3: scope memo. Systems in and out of scope, data classes, TSC categories (usually Security), target report type.
- Days 2–5: owners matrix. Put names on the table above and hold a weekly 30-minute check-in.
- Days 3–10: minimum policy set. Information security, access control, change management, incident response, acceptable use, vendor management, all short and accurate.
- Days 5–14: close obvious gaps. Enforce MFA everywhere material, remove shared admin passwords, turn on audit logs, document offboarding.
- Days 7–18: vendor inventory. List subprocessors and critical tools, store contracts, note which vendors publish SOC reports.
- Days 10–21: evidence plumbing. Decide spreadsheet or compliance automation. If you evaluate platforms, read Vanta vs Drata vs Secureframe and Sprinto vs Vanta, then confirm current packaging on vendor sites.
- Days 14–25: internal dry run. Pick 10 controls from the CC1–CC9 table and assemble evidence as if the auditor asked today.
- Days 21–30: auditor shortlist. Interview CPA firms using the checklist below and agree scope, report type, period, and delivery date.
How to vet your SOC 2 auditor in 2026
Takeaway: A cheap, instant report from a firm you cannot verify can hurt you with buyers; check license, peer review, and independence first.
In 2026 the AICPA put SOC report quality front and center. Its SOC page carries a notice that it is looking into anonymously published allegations about a compliance vendor offering SOC services. The same page links to AICPA coverage such as “Promises of ‘fast and easy’ threaten SOC credibility” (dated February 1, 2026), and the Journal of Accountancy ran a podcast, “The risks of quick-turn SOC engagements” (April 30, 2026). It also reported in May 2026 that the AICPA guides peer reviewers to address SOC 2 risks, including engagements with identical reports, risk assessments, sample sizes, and testing across clients.
| Check | How to verify | Red flag |
|---|---|---|
| The signing firm and CPA are licensed | Look them up on NASBA’s CPAverify or the relevant state board | No licensed US CPA firm named on the report |
| The firm is enrolled in peer review | Ask for the latest peer review report and its rating | Firm won’t share or isn’t enrolled |
| The auditor is independent of your tool vendor | Ask who sets the audit fee and who controls evidence access | Bundled “tool + audit” price set by the platform, or the platform sits in on auditor discussions |
| Testing is tailored to your system | Ask how they assess risk and choose samples for your environment | Templated report promised before fieldwork |
| The timeline is realistic | Compare with the phases above | A Type 2 “in days” or a guaranteed clean opinion |
Your enterprise buyers’ security teams read SOC reports for a living. A report from an unverifiable firm can trigger more questions than having no report at all.
Where compliance automation fits
Takeaway: Automation collects evidence; it does not replace owners or the CPA firm.
Vanta, Drata, Secureframe, Sprinto, and similar tools connect to your cloud, identity provider, code host, and HR system to collect evidence, flag failing tests, and share it with auditors. They help small teams, but buyers want the auditor’s report, not a dashboard. Before you buy, ask: does it integrate with most of our stack, who clears failing tests every week, does our chosen auditor work with it, and are we paying for frameworks we won’t use this year? Pricing is usually quote-based, so compare written quotes rather than third-party estimates. Our comparisons: Vanta vs Drata vs Secureframe and Sprinto vs Vanta.
Common SOC 2 readiness mistakes
Takeaway: Most failures come from scope and ownership, not missing software.
- Buying automation before writing scope and naming owners.
- Copying policy templates that contradict how engineering actually ships.
- Starting a Type 2 period while access reviews and logging are still broken.
- Promising Availability or Privacy in sales decks without putting them in scope.
- Skipping vendor risk because “everyone uses AWS and Google Workspace.”
- Choosing an auditor on price and speed alone.
- Treating the first report as the finish line instead of an annual cycle.
Write the system description early
Takeaway: A one-page boundary keeps engineering, sales, and the auditor describing the same system.
Draft a one-page system description: products and environments in scope, hosting regions and major cloud services, identity providers, the CI/CD path to production, data stores holding customer content, and subprocessors that touch it. List what is out of scope (marketing site, old staging experiments, acquired tools not yet integrated). Unclear boundaries cause two problems: infrastructure changes during the review period break evidence continuity, and sales over-promises (“the whole company is SOC 2”) when the report covers one product. The AICPA’s Description Criteria define what the formal description must include, so expect your auditor to refine it.
Customer trust workflows while you wait
Takeaway: Honest artifacts and dates beat a vague “SOC 2 in progress.”
Deals keep moving during readiness. Keep a controlled answer library for questionnaires, a named security contact (a form or role-based channel works), an exportable subprocessor list, and a process for sharing reports or bridge letters under NDA once you have them. Make sure questionnaire answers match your public privacy policy and terms. If you have a Type 1 and a Type 2 period underway, say so with dates.
FAQ
1) When does a SaaS startup need SOC 2?
Usually when enterprise procurement, security questionnaires, or contracts make a SOC 2 report a practical requirement, or when you handle sensitive customer data and buyers expect formal assurance. Before that, invest in security basics.
2) Is SOC 2 a certification?
No. People say “SOC 2 certified,” but SOC 2 is an attestation examination that ends in a CPA firm’s report against the Trust Services Criteria for a defined system and date or period.
3) What are the SOC 2 compliance requirements for a first report?
For a Security-only report, the requirements are the common criteria CC1–CC9 in the 2017 TSC (with 2022 revised points of focus) plus a system description that meets the AICPA Description Criteria. How you meet each criterion is up to your controls; the auditor tests them.
4) Should we start with Type 1 or Type 2?
Type 1 if a buyer accepts design-only assurance and the deal can’t wait; Type 2 if the buyer requires operating effectiveness and you can support a review period. See SOC 2 Type 1 vs Type 2.
5) How long does SOC 2 take for a startup?
A focused readiness sprint can take about a month if basic controls exist. A Type 2 report adds a review period that practitioners commonly set between 3 and 12 months, plus fieldwork. Your CPA firm sets the actual dates.
6) Do we need Vanta, Drata, or another tool?
No tool is required. Automation cuts manual evidence work for small teams; disciplined teams have completed SOC 2 with spreadsheets.
7) How do we know an auditor is legitimate?
Confirm the firm and signing CPA on CPAverify or the state board, ask for its peer review report, and make sure the audit fee and evidence access are not controlled by your tool vendor.
8) Is this audit or legal advice?
No. It is educational content. Engage a qualified CPA firm for the examination and counsel for contracts and regulatory questions.
Bottom line
SOC 2 readiness is an ownership and evidence problem first and a tooling problem second. Put Security in scope, assign owners, check yourself against CC1–CC9, choose Type 1 or Type 2 based on real buyer demand, and vet the CPA firm as carefully as you vet any vendor.
Next step: decide your report path with SOC 2 Type 1 vs Type 2, then shortlist automation in Vanta vs Drata vs Secureframe. For the company-level picture, see the SaaS founder compliance checklist, Start here, and Tools.
Sources (checked October 5, 2026): AICPA & CIMA SOC 2 page; 2017 TSC (revised points of focus 2022); Journal of Accountancy, May 2026; Journal of Accountancy podcast, April 30, 2026; NASBA CPAverify.